- Cybersecurity
- Data Protection
- PDPL
- ECC-2:2024
- Regulatory Compliance
- National Cybersecurity Authority
- E-commerce
- Cybersecurity and Data Protection
No Excuse for Ignorance: A Business Guide to Cybersecurity and Data Protection in Saudi Arabia
A practical guide for companies in Saudi Arabia explaining the cybersecurity and data protection regulatory landscape. It covers the Personal Data Protection Law (PDPL), Essential Cybersecurity Controls (ECC-2:2024), sector-specific requirements
- Client
- Companies and organizations in Saudi Arabia
- Duration
- 90-day implementation plan
- Services
- Cybersecurity Readiness Assessment · PDPL Compliance Review · ECC-2:2024 Controls Review · Gap Identification and Remediation Prioritization · 90-Day Implementation Plan
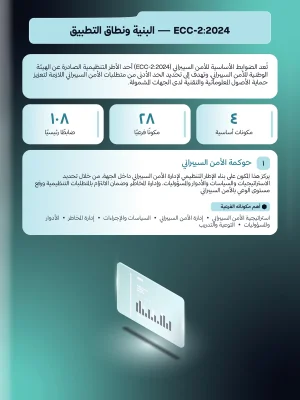
- 4
- Core components in ECC-2:2024
- 28
- Sub-components
- 108
- Main controls
- 90
- Days in the implementation plan
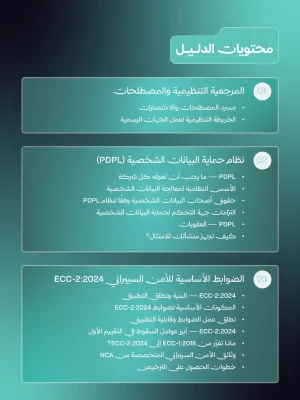
01
Regulatory Reference and Terminology
Explains the official bodies responsible for regulating cybersecurity and data protection in the Kingdom, their mandates, key terminology and acronyms, and a regulatory map to help organizations identify the requirements relevant to their activities.
02
Personal Data Protection Law (PDPL)
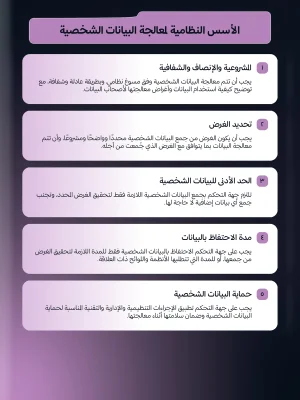
Explains what the law requires of companies, from the legal bases for processing personal data and data subject rights to controller obligations, penalties, and the steps needed to prepare for compliance.
03
Essential Cybersecurity Controls (ECC-2:2024)
Reviews the structure, components and scope of the controls issued by the National Cybersecurity Authority, common reasons for failing an initial assessment, changes between ECC-1:2018 and ECC-2:2024, specialized regulatory documents, and licensing steps.
04
Cybersecurity by Sector
Explains how requirements differ by business activity, covering the financial sector (SAMA and CMA), healthcare, telecommunications and ICT, and e-commerce data protection requirements.
05
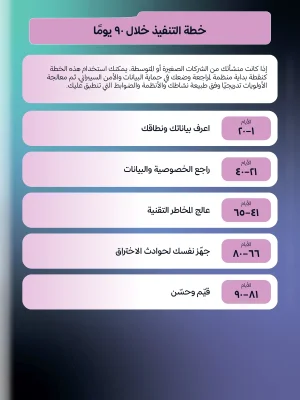
90-Day Implementation Plan
A phased plan that starts with identifying data and scope, then reviewing privacy practices, addressing technical risks, preparing for security incidents, and completing an evaluation and improvement stage.
06
Most Common Mistakes
Highlights practices that may create compliance gaps, including the absence of an incident reporting plan, reliance on outdated control versions, and the use of production data in development and testing environments, along with suggested fixes.
07
Sources and References
Lists the official sources referenced in the guide, including laws, regulations, and controls issued by the relevant authorities.
Pages from the report
Other case studies
Digital Government
Digital Government Authority Compliance Guide
Government entities and digital platform providers in Saudi ArabiaPDF ↓